France Flags 3 Vendors as Fridge-Hack Risk Lingers [2026] – shattered.io
France’s cybersecurity agency has formally contacted a Danish equipment vendor over a software flaw at the center of the weekend cyberattack that knocked out refrigeration at hundreds of French supermarkets, according to a person close to Prime Minister Sebastien Lecornu. The move, confirmed Monday, marks the first official acknowledgment of which company’s technology sits at the root of an attack that spoiled food, triggered fires, and left investigators with no named suspects five days later.
The overnight Sunday-to-Monday intrusion, which hit refrigeration systems at Intermarché, Coopérative U, Carrefour, Monoprix, and E.Leclerc, has already generated several rounds of coverage focused on store counts and spoiled inventory. What has received less attention is the government-to-vendor escalation now underway, and a warning from France’s cyber agency that the campaign was “likely still underway” even as cleanup crews worked through the damage. That warning, more than the temperature readings, is what should worry retailers and industrial operators far outside France.
The attack unfolded overnight between Sunday and Monday, October 12, hitting refrigeration controllers across multiple French supermarket chains at once. A spokesperson for Groupement Mousquetaires said roughly 150 Intermarché stores were affected. Coopérative U reported almost 100 locations hit. Carrefour said about 80 of its supermarkets were affected, while stressing that most of its roughly 6,000 stores in France were untouched. Monoprix said about 5% of its roughly 490 French stores were affected.
The Shattered Newsletter
The week’s biggest stories in tech, gaming and security, in one email.
Free, once a week. Unsubscribe any time.
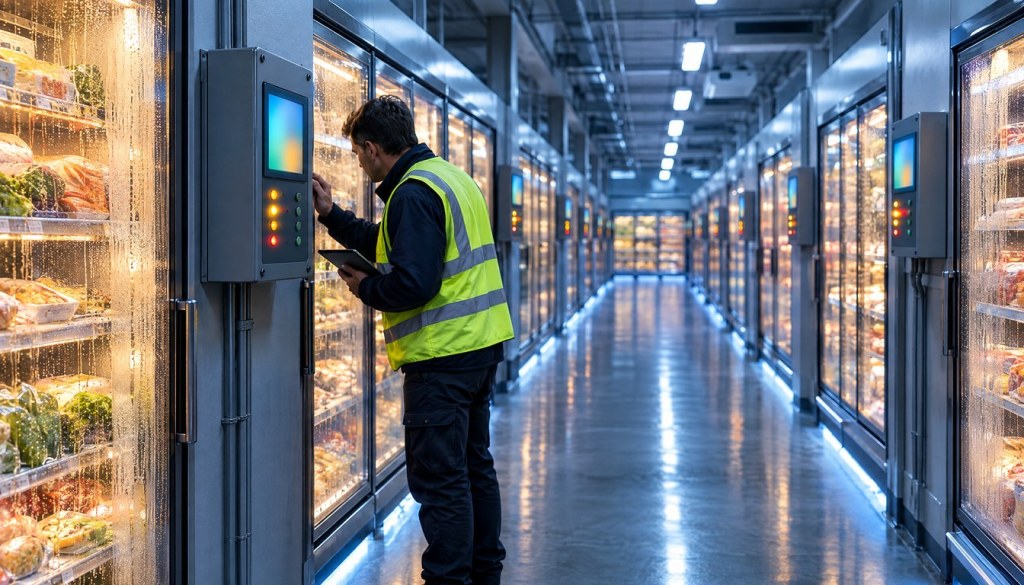
Inside the affected stores, refrigerators and freezers reportedly climbed to as high as 50°C, or 122°F, and stayed there for about six hours before staff could intervene. Fresh meat, frozen goods, and produce had to be thrown out across the affected locations, and fires were reported at some sites as equipment strained under the unexpected heat load, according to French media. For a sector that runs on tight cold-chain margins, six hours at that temperature is enough to destroy an entire day’s perishable inventory in a single store.
The scale of the disruption, hitting five major retail groups in a single night, is what pushed this beyond a routine IT outage and into the territory of a coordinated industrial control system attack, according to reporting from CNBC.
France’s cybersecurity agency identified the refrigeration systems involved in the attack as products from three manufacturers: Danfoss, Copeland, and Dixell. Naming three separate vendors in the same incident suggests the weakness was not isolated to one company’s product line but reflects a broader pattern across the refrigeration-controls industry, where similar architectures and remote-management protocols get reused across competing brands.
Of the three, Danfoss has drawn the most scrutiny, partly because it was first to issue a public statement and partly because investigators pointed to two of its specific product lines as implicated in the intrusion. Copeland and Dixell have not detailed their own exposure publicly in the same way, and it remains unclear whether the vulnerabilities across all three vendors share a common root cause or are three separate flaws that happened to surface in the same attack window.
Researchers at industrial-security firm Claroty, which studies vulnerabilities in operational technology, said the flaw at issue could let an attacker remotely reach into a refrigeration management system and alter settings, including “to change any setting, including the operating temperature of the refrigeration system,” according to Claroty Chief Technology Officer Amir Preminger. That description lines up with what store staff reported: units silently climbing far past their normal operating range with no obvious external trigger.
Danfoss has publicly named two of its own product lines as the specific systems implicated in the French attack: the AK-SM800 and AK-SC355 refrigeration regulator systems. Both are supervisory controllers widely used to manage banks of commercial refrigeration units from a central panel, the kind of equipment that lets a single store manager or a remote facilities team monitor dozens of fridges and freezers at once rather than checking each unit by hand.
That centralization is exactly what made the systems attractive to whoever carried out the attack. A controller that can adjust the operating temperature of an entire bank of units from one interface is also a single point of failure if an attacker gains unauthorized access to it. Danfoss said in a statement that it was “aware of incidents in France affecting a limited number of refrigeration management systems,” language that leaves open how many total units across the country were ultimately touched.
Danfoss also described the vulnerabilities in stark terms, saying “these vulnerabilities should be considered serious,” a characterization that, combined with the company’s own admission about the age of the affected gear, points toward a problem that goes well beyond a single bad patch.
Danfoss’s own explanation for why the attack succeeded centers on firmware age, not a brand-new zero-day. The company said the affected units were running “outdated firmware” and that most of the implicated equipment was legacy hardware that no longer received software or security updates at all. In other words, the vulnerability that attackers exploited was not freshly discovered in the way a zero-day typically is. It was a known weak point sitting on equipment that had aged out of the vendor’s support window.
Danfoss said it had “long advised customers to keep supported systems updated with the latest firmware and to migrate legacy systems to current-generation solutions,” a statement that puts the burden of the fix squarely on store operators and the chains that manage their equipment contracts, rather than on the vendor shipping a new patch.
That framing matters for how the rest of the retail and industrial sector should read this incident. Refrigeration controllers are not the kind of equipment that gets swapped out on a two-year refresh cycle like a point-of-sale terminal. Commercial refrigeration systems are built to run for a decade or more, and the controllers overseeing them often get installed once and left alone unless something breaks. That makes “migrate to current-generation solutions” a far more expensive and disruptive ask for a supermarket chain running thousands of locations than it sounds on paper.
The detail that separates this story from a typical post-incident writeup is the agency’s own uncertainty about whether the attack had actually stopped. France’s cybersecurity agency warned that the attacks were “likely still underway,” a phrase that pushes this from a contained, past-tense incident into an active, ongoing one. ANSSI Director Vincent Strubel underscored that uncertainty directly, saying “we do not yet have a detailed understanding of the sabotage attacks targeting these systems since last night,” according to Le Monde.
That kind of language from a national cyber agency is not boilerplate caution. It signals that investigators had not yet mapped the full scope of affected systems, could not rule out additional stores or chains getting hit, and had no way to guarantee that remediation at one site would hold if the underlying vulnerability remained unpatched elsewhere. For any supermarket chain or logistics operator running Danfoss, Copeland, or Dixell equipment outside France, that warning is the single most actionable piece of information in the entire story.
It also explains why the government moved as fast as it did on the vendor-notification front. Reaching out to the Danish company behind the flawed software is not just about getting a patch written. It is about trying to close a door that, as of the agency’s own statement, may still have been open.
A person close to Prime Minister Sebastien Lecornu said France’s cybersecurity agency had identified “a vulnerability in software supplied by a Danish company and has contacted the vendor.” That brief line is, in effect, the government’s confirmation that this was not a diffuse, unattributable infrastructure failure. It was a specific, identifiable software weakness, traced to a specific supplier, with a formal government-to-vendor conversation now underway.
Government-level vendor outreach of this kind typically happens when the exposure extends beyond the immediate victims. Danfoss sells refrigeration controls globally, not just in France, which means any fix the company ships as a result of this contact will likely apply to installations well outside the French supermarkets currently in the headlines. That is also why Danish authorities, not just French ones, are likely to end up involved in whatever technical disclosure process follows.
The episode is a reminder that operational technology vulnerabilities rarely stay contained to the sector where they were first discovered. A refrigeration controller sold into French grocery chains uses the same underlying remote-management software as the same controller sold into Danish dairies, German cold-storage warehouses, or US grocery distribution centers. A government contacting a vendor over a French incident is, functionally, a government forcing a fix that every other customer of that vendor benefits from too.
Five days after the attack began, no group had claimed responsibility, and prosecutors had not identified the perpetrators. That absence of attribution is itself a data point. Ransomware crews and hacktivist groups that disrupt retail or industrial targets typically claim credit quickly, either to extort a ransom or to make a political statement. Silence this long after an attack that generated international headlines suggests either a more cautious, financially unmotivated actor, or a group waiting to see how much damage the disruption causes before deciding whether to surface.
Deputy national cybersecurity coordinator-level officials in France, speaking about the broader pattern of unpatched industrial equipment, described the underlying vulnerability as “an accident waiting to happen,” adding that “people simply hadn’t patched their equipment.” That assessment frames the incident less as a sophisticated nation-state operation and more as an avoidable failure of basic patch hygiene colliding with equipment that, as Danfoss itself acknowledged, had aged out of support entirely.
Al Jazeera’s reporting on why supermarkets specifically have become attractive targets for this kind of disruption points to the same structural issue: large retail chains run enormous fleets of decades-old operational equipment that was never designed with network security in mind, and that equipment is increasingly exposed to the internet for remote monitoring convenience, according to Al Jazeera.
France’s cybersecurity agency issued direct guidance to affected and potentially affected businesses in the wake of the attack. The agency urged operators to use a secure VPN or a protected network when managing refrigeration systems remotely, to install firmware updates on all supported equipment immediately, and to change passwords on any system that controls industrial or refrigeration equipment.
Those three steps sound basic, almost too basic for an attack that spoiled food at hundreds of stores and forced a national cyber agency to contact a foreign vendor. But that is precisely the point investigators keep returning to: this was not a zero-day requiring months of research to discover. It exploited systems that were already known to be outdated, reachable without a VPN, and in some cases still running factory-default or long-unchanged credentials.
For a security team at a grocery chain, a logistics company, or any business running refrigerated cold storage, those three guidance points double as an immediate audit checklist. Any refrigeration controller reachable without a VPN is an exposed controller. Any controller not receiving firmware updates is running on borrowed time. And any system still using default or years-old passwords is one credential-stuffing attempt away from the same outcome French supermarkets experienced this week.
The reported scale of the disruption varies meaningfully by chain, both in raw store counts and as a share of each company’s total French footprint. The table below summarizes what each retailer has disclosed so far.
Even with incomplete figures from two of the five named chains, the pattern is clear: this was not an attack against a single company’s infrastructure. It hit a shared class of refrigeration-control technology deployed across competing retail groups, which is exactly what makes the vendor-level response, rather than a chain-by-chain fix, the only response that can actually close the gap.
The French fridge hack fits into a recognizable, if uncomfortable, lineage of attacks against operational technology and industrial control systems. What distinguishes it from most of its predecessors is the target: not a power grid, a pipeline, or a nuclear facility, but a grocery store’s refrigeration unit, the kind of equipment nobody in corporate IT typically thinks to put on a patch-management schedule.
Each prior incident on that list targeted equipment with an obvious safety or economic catastrophe attached to it, which is why they drew sustained government attention. Refrigeration controllers do not carry that same immediate danger profile, which may be exactly why they went unpatched for so long. This attack suggests that attackers are willing to go after lower-profile OT targets precisely because the defenses around them are thinner.
The immediate financial hit from this attack lands in two places: wasted inventory and, for some locations, fire damage. Food retailers run on thin margins already, and losing a full day’s worth of fresh and frozen stock across more than 400 stores combined is not a cost any single chain can shrug off, even before factoring in cleanup, repair, and potential equipment replacement.
The longer-term market impact sits with insurers and with the vendors who sell OT security tools. Property and business-interruption insurers covering grocery and cold-storage clients are now facing a concrete, recent, well-documented loss event tied specifically to unpatched refrigeration controllers, which gives underwriters a hard data point to justify tighter policy language around OT patch compliance going forward.
For vendors selling OT and industrial control system security products, Danfoss’s own admission that its customers were running equipment with no software support left is close to a worst-case advertisement for the category. Expect procurement conversations at major retail chains to shift from “do we need OT visibility tools” to “how fast can we deploy them,” particularly for any chain running refrigeration, HVAC, or building-management systems from the same supplier pool implicated here.
The pattern behind this attack is not new. Industrial control systems across sectors, from power utilities to water treatment to manufacturing, have repeatedly been exposed as running on equipment that predates modern network security practices by a decade or more. What changes from incident to incident is which sector gets caught holding the oldest, least-monitored equipment at the moment an attacker goes looking.
Retail refrigeration had largely escaped that scrutiny until now. Supermarket chains buy and install refrigeration systems to last, often for a decade or longer, and once installed those systems tend to disappear from the corporate IT department’s radar entirely. They get managed by facilities teams, maintained by third-party contractors, and rarely touched by the security staff who handle point-of-sale systems, payment processing, or customer data.
That organizational blind spot, equipment that exists physically inside a company’s stores but operationally outside its security team’s visibility, is the common thread linking this attack to the broader history of OT and ICS incidents. Fixing it requires treating refrigeration, HVAC, and other building-management systems as first-class assets in a company’s security inventory, not an afterthought handled by a separate facilities budget.
The public statements from officials and researchers involved in this incident paint a consistent picture: a known class of vulnerability, sitting on unsupported equipment, that nobody had gotten around to fixing. Claroty’s Amir Preminger described the practical danger of the flaw directly, explaining that attackers could use it “to change any setting, including the operating temperature of the refrigeration system,” a capability that matches exactly what played out across the affected stores, according to Le Monde’s reporting.
ANSSI Director Vincent Strubel’s comment that investigators did not yet have “a detailed understanding of the sabotage attacks targeting these systems since last night” reflects how early-stage this investigation still was, even days after the first reports surfaced. Danfoss, for its part, did not shy away from the severity of the issue, stating plainly that “these vulnerabilities should be considered serious,” according to reporting from CBC.
Danfoss’s own explanation of the root cause, that affected units ran “outdated firmware,” and that it had “long advised customers to keep supported systems updated with the latest firmware and to migrate legacy systems to current-generation solutions,” according to ABC News Australia, puts the responsibility question squarely in the hands of operators who kept running equipment the vendor no longer supported.
Five companies, three named equipment vendors, one government contacting a foreign supplier, and an agency warning that the campaign might still be running. That combination of facts is unusual for a retail cyberattack story, which typically wraps up once the immediate outage is fixed. Here, the technical root cause (unsupported firmware on shared industrial controllers) guarantees that any store, warehouse, or distribution center running the same hardware anywhere in the world carries the same exposure until a patch actually ships and gets installed.
That is the real story behind the headlines about spoiled meat and overheated freezers: an entire category of industrial equipment that retailers, insurers, and regulators had not been treating as a serious attack surface now has a very public, very expensive case study proving that it is one. Bloomberg’s coverage of the weekend disruption noted the attack hit refrigeration sites across multiple chains simultaneously, a detail that underscores just how widely shared this exposure runs across the industry, according to Bloomberg.
What caused the French supermarket fridge hack?
Investigators traced the attack to a vulnerability in refrigeration management software made by Danfoss, Copeland, and Dixell. Danfoss said the affected units were running outdated firmware and that much of the implicated equipment was legacy hardware no longer receiving software or security updates.
Which supermarket chains were affected?
Intermarché, Coopérative U, Carrefour, Monoprix, and E.Leclerc were all named as affected. Reported scale varies: roughly 150 Intermarché stores, almost 100 Coopérative U locations, about 80 Carrefour supermarkets, and roughly 5% of Monoprix’s approximately 490 France stores.
Which Danfoss products were specifically named?
Danfoss identified its AK-SM800 and AK-SC355 refrigeration regulator systems as the specific product lines implicated in the French incidents.
Is the fridge-hacking attack still active?
France’s cybersecurity agency warned that the attacks were “likely still underway” as of its public statement, and as of this report, no group had claimed responsibility and prosecutors had not identified the perpetrators.
What is France’s government doing about the vulnerability?
A person close to Prime Minister Sebastien Lecornu said France’s cybersecurity agency identified a vulnerability in software from a Danish company and had contacted that vendor directly, in addition to issuing guidance to affected businesses.
What guidance has France issued to businesses?
The cybersecurity agency urged affected and potentially affected businesses to use a secure VPN or protected network, install available firmware updates immediately, and change passwords on systems controlling refrigeration or other industrial equipment.
Should retailers outside France running Danfoss, Copeland, or Dixell equipment be worried?
Given that these vendors sell globally and the vulnerability was tied to firmware age rather than a France-specific configuration, any business running the same legacy controller generations elsewhere faces comparable exposure until vendor patches are issued and applied.
The Shattered Newsletter
The week’s biggest stories in tech, gaming and security, in one email.
Free, once a week. Unsubscribe any time.
Daniel Roth covers cryptocurrency and the cryptography behind provably-fair systems, explaining how commitment schemes and verification actually work rather than how they are marketed.
Independent explainers on cryptography, security, privacy and the technology behind provably-fair systems. Home of the original SHA-1 collision research.
The Shattered Newsletter: the week’s biggest stories in tech, gaming and security.
source
This is a newsfeed from leading technology publications. No additional editorial review has been performed before posting.